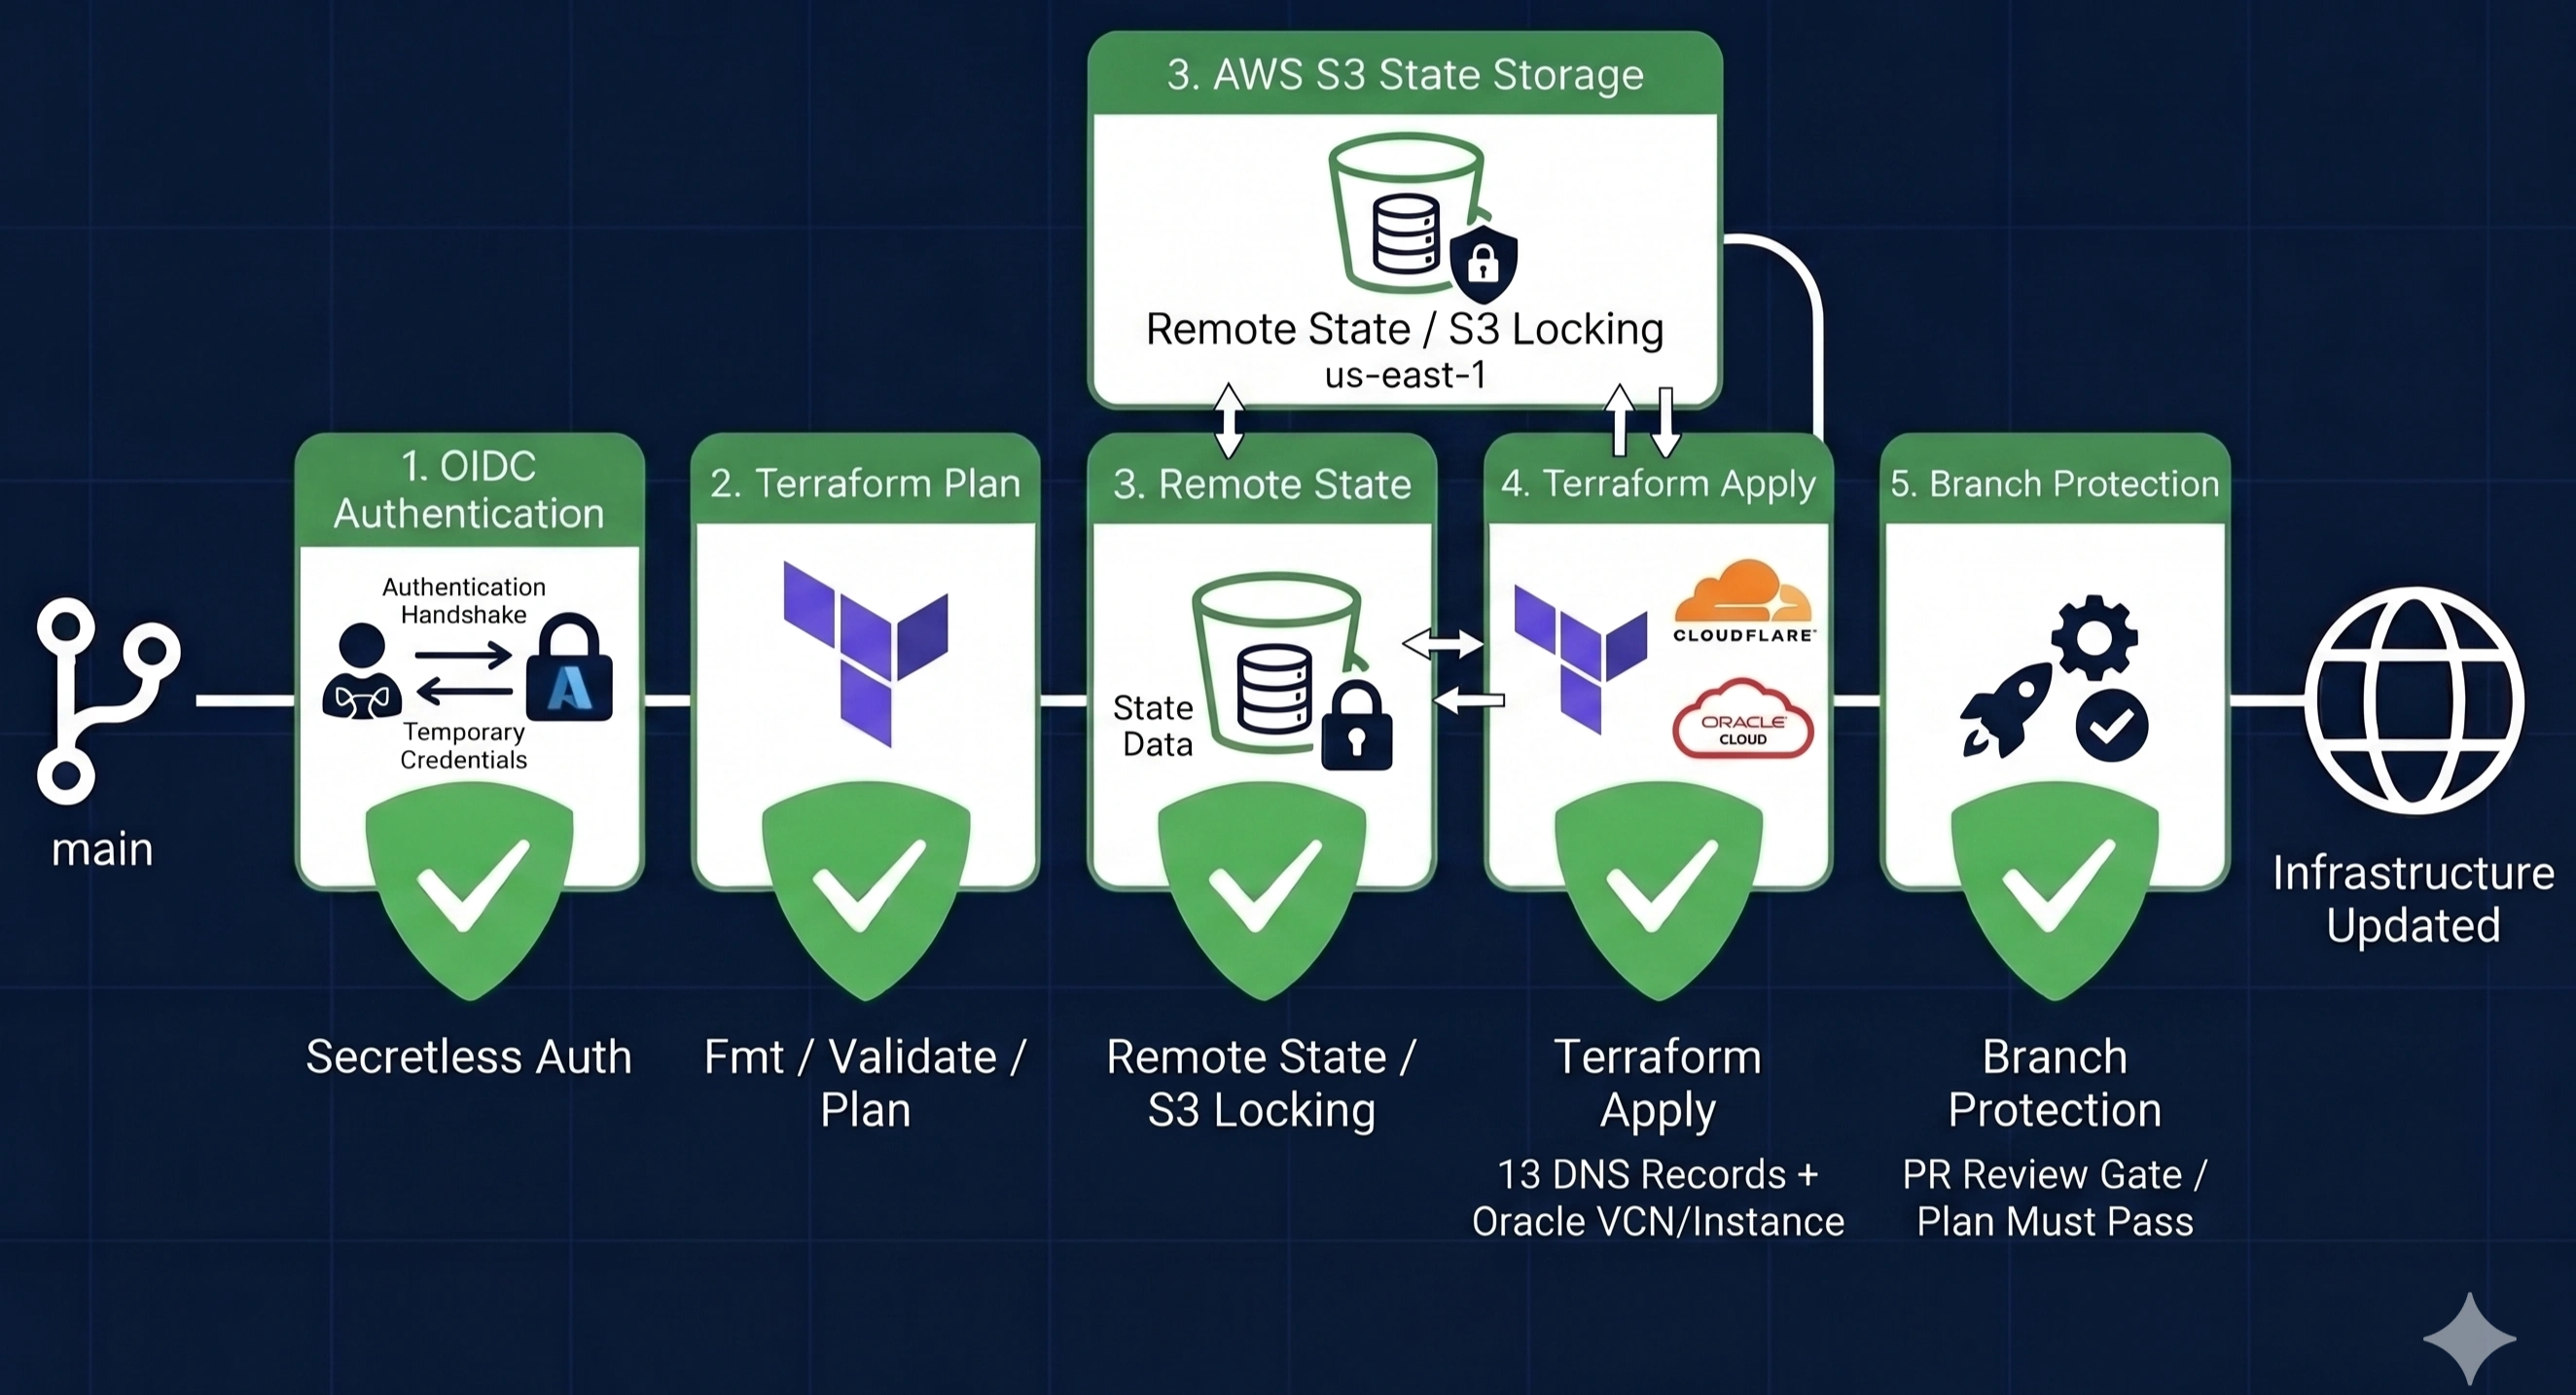
A five-stage GitOps pipeline diagram showing a Terraform deployment workflow. The stages, marked with green checkmarks, include OIDC Authentication, Terraform Plan (Fmt/Validate/Plan), AWS S3 Remote State Locking, Terraform Apply (deploying 13 DNS records and an Oracle VCN/Instance), and Branch Protection. The pipeline concludes with an 'Infrastructure Updated' globe icon.

Part 2: Infrastructure as Code with Terraform, OIDC, and a GitOps Pipeline

How I brought my hybrid cloud homelab under Terraform management — 13 Cloudflare DNS records, an Oracle Cloud instance, remote state in AWS S3, and a GitHub Actions pipeline with secretless OIDC authentication. No more clicking around in dashboards.
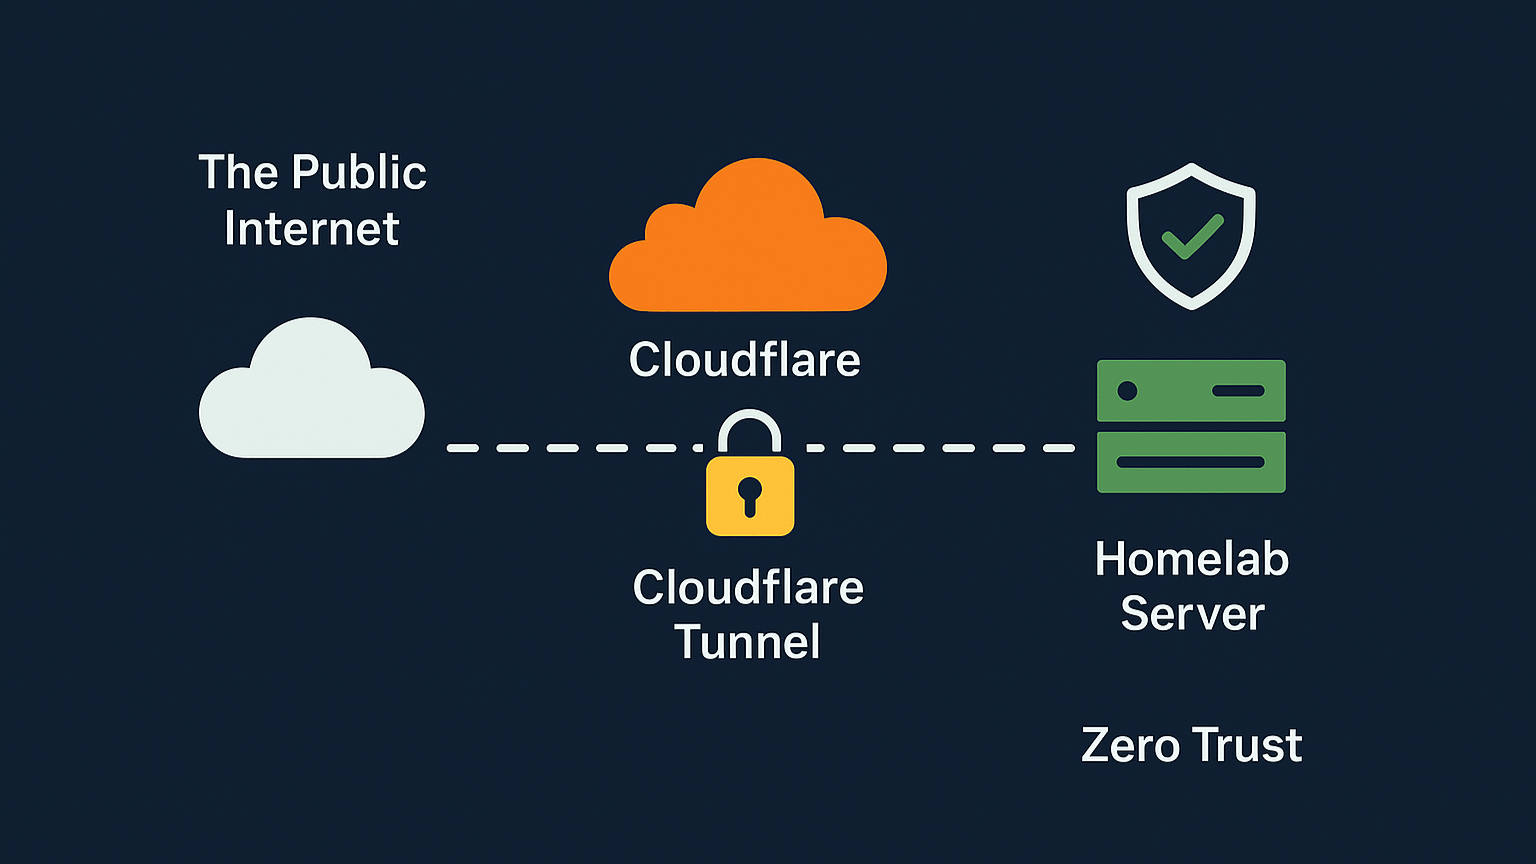
A diagram of a Zero Trust architecture, showing how a Cloudflare Tunnel securely connects a homelab server to the public internet via Cloudflare's network.

Part 5: Securing a Homelab with Cloudflare Tunnels and Zero Trust

Learn how to build a secure, globally-accessible homelab using a Cloudflare Tunnel. This guide covers implementing a Zero Trust security model to protect your services and eliminate the need for open router ports.